
Project ManagerOctober 27, 2026
SDLC stands for software development life cycle. It is the framework that describes every step a piece of software goes through, from the first idea to launch and long-term maintenance. If you have ever asked what SDLC means, the short answer is this: it is a structured way to plan, build, test and release software so that the result is predictable, secure and useful.
In this guide we explain what SDLC is, why it matters, the six phases most teams use, the main SDLC models (Waterfall, Agile, Spiral and V-model), how security fits in, and what the process looks like in a real mobile app project.
What Is SDLC?
The software development life cycle (SDLC) is a process framework that defines which steps a software project follows, who does what in each step and when a step counts as finished. Its purpose is to deliver working software on a realistic timeline, within budget and at the quality the business expects.
The framework works because it reduces uncertainty. Without a defined process, requirements become clear too late, testing gets squeezed into the last week and delivery dates slip. SDLC makes those risks visible at the start, when they are still cheap to fix.
One distinction is worth making early. SDLC is a framework, not a single method. Questions such as “Waterfall or Agile?” are about which SDLC model you choose. Whichever model you pick, the same phases still happen. They only differ in order, length and how often they repeat.
Why SDLC Matters
A conscious life cycle gives a team three concrete benefits:
Predictability: When the output of each phase is clear, time and cost can be estimated more honestly.
Quality: Testing and review are built in from the start, so defects are caught early, when they are cheapest to fix.
Shared language: Product owners, designers, developers and clients use the same phase names, which keeps expectations aligned.
The cost of a defect grows with the phase in which it is found. A misunderstanding that could have been fixed with one sentence during requirements can turn into months of rework after release.
The Phases of SDLC
Sources list between five and seven phases. The six below are the most common breakdown.
1. Planning
The team defines why the project exists, who it serves, its scope, budget and timeline. Feasibility is checked here: can this product be built technically, financially and operationally? The usual output is a project plan and a scope document.
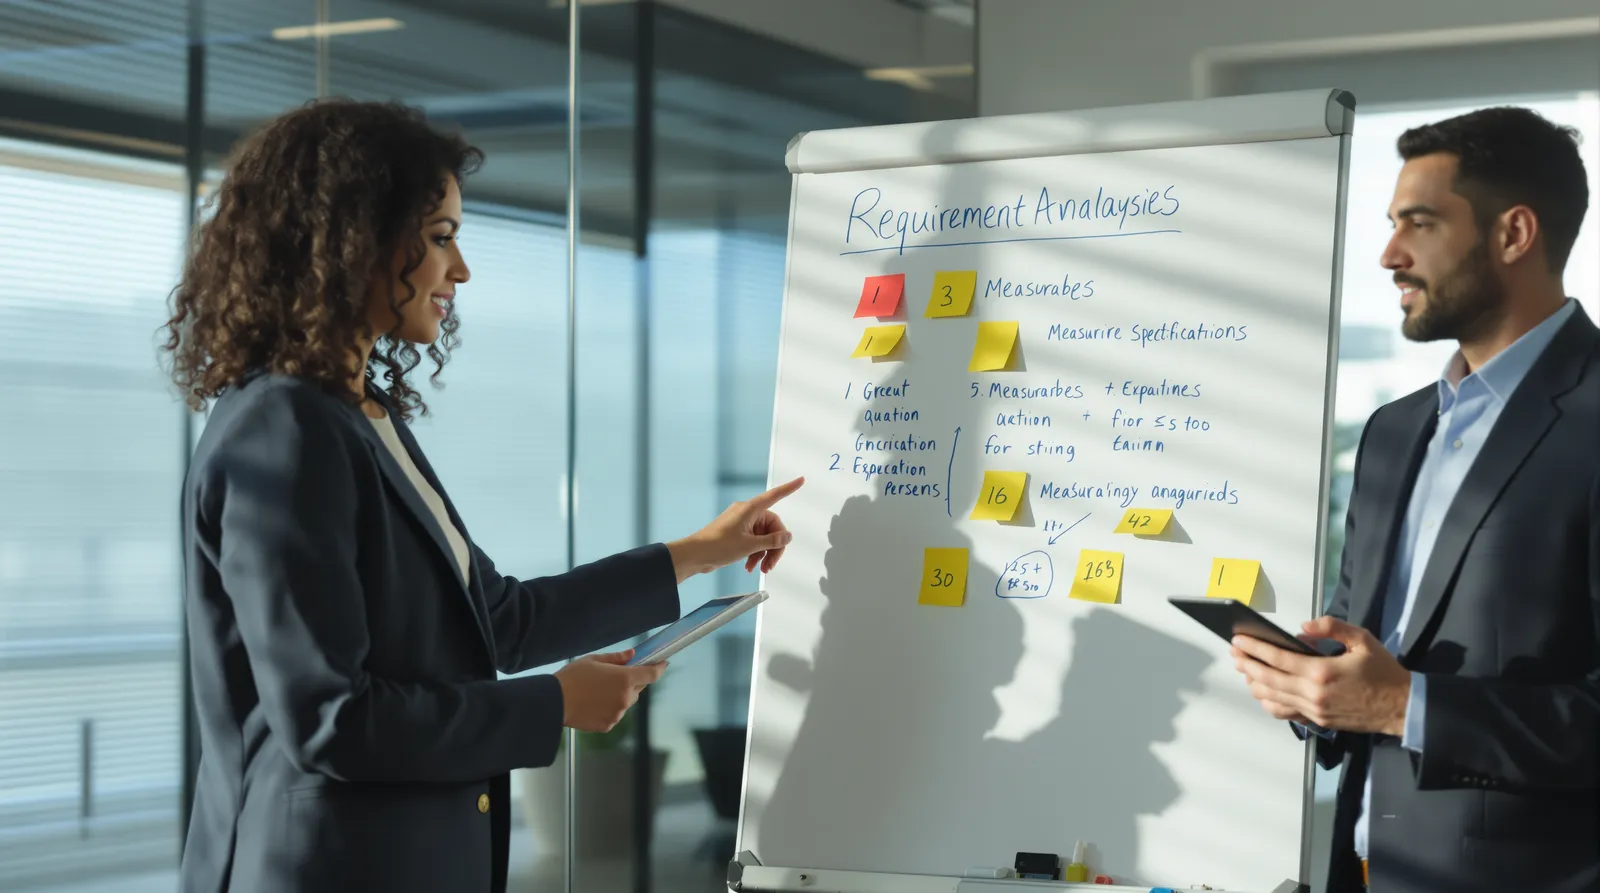
2. Requirements Analysis
Business goals, user needs and technical constraints are turned into written requirements. A good requirement is measurable. Instead of “the app should be fast,” a team writes “the home screen loads in under two seconds.” We cover this step in detail in how to turn business goals into technical requirements. Clarifying the real problem the product must solve is part of product discovery.
3. Design
Both the interface and the technical architecture are designed. On the interface side, the team prepares flows, screens and a design system. On the technical side, it decides on the database, services, APIs and security approach. The outputs are design files and an architecture document.
4. Development
The design becomes code. The team splits work into small pieces, keeps code in version control and reviews each other’s changes. This is usually the longest phase, yet it holds the fewest surprises when the first three phases were done well.
5. Testing
The team verifies that the software meets its requirements. Unit tests check small pieces of code, integration tests check that parts work together and acceptance tests check that the product meets the client’s expectations. Performance and security testing belong here too.
6. Deployment and Maintenance
The product goes live. For a mobile app, this includes submission to the App Store and Google Play and the review process that comes with it. Release is not the end but the start of a new loop: bug fixes, security patches, operating system updates and new features continue under maintenance and support.
SDLC Models Compared
The phases stay the same, but the order and rhythm depend on the model. These are the most widely used SDLC methodologies.
Waterfall Model
Phases follow one another in a straight line, and a phase does not start until the previous one ends. When requirements are fixed and well understood, for example in a regulated enterprise system, it gives a predictable, well-documented path. Its weaknesses are that users see the product late and that late changes are hard to absorb.
Agile Model
The project is split into short cycles, often two to four weeks long, called sprints. Each sprint repeats planning, development and testing at small scale and produces a working piece of the product. Agile adapts well to changing priorities. Scrum and Kanban are its best-known forms. If you are weighing the two approaches, our Agile vs Waterfall decision guide can help.
Spiral Model
The Spiral model repeats the cycle with a strong focus on risk analysis in every loop. It suits large, expensive or high-risk projects where risk must be re-evaluated at each step. It is heavier than needed for small projects.
V-Model
The V-model is a test-driven variant of Waterfall. Every development phase has a matching testing phase. It is used where safety is critical and a defect is unacceptable.
Model | Structure | Adapts to change | Best for |
Waterfall | Linear, phase by phase | Low | Fixed scope, documentation-heavy projects |
Agile | Short, repeating cycles | High | Product-led projects with changing priorities |
Spiral | Risk-driven loops | Medium | Large, high-risk projects |
V-model | Linear with matching test phases | Low | Safety and reliability critical systems |
Most product teams today do not apply one model in pure form. They keep Agile as the general frame and borrow Waterfall-style clarity for critical parts such as payments or security. CI/CD practices speed the cycle up further, and our guide on DevOps best practices explains how teams set that up.
Secure SDLC
Security should not be a final checkbox. A secure SDLC adds security activities to every phase:
Requirements: Define data protection, authentication and compliance needs.
Design: Model threats and choose a safe architecture.
Development: Follow secure coding rules and scan dependencies.
Testing: Run security tests and penetration tests.
Maintenance: Patch vulnerabilities and monitor for incidents.
For mobile projects, the most common threats and how to prevent them are covered in our guide to mobile app security.
SDLC in a Mobile App Project
The phases are the same in mobile development, but mobile adds its own decisions. Neon Apps has delivered iOS, Android and cross-platform projects since 2019. In practice, the flow looks like this:
Discovery: Target users, competitors and the scope of the first release are defined. Many teams start with an MVP to learn quickly.
Design: Flows and prototypes follow platform guidelines for iOS and Android. See our mobile app design guide for the details.
Development: The team chooses native or cross-platform and builds the backend and APIs alongside the app.
Testing: The app is tested across devices and OS versions, and security is checked separately.
Release: Store requirements, privacy declarations and review time are part of the plan. Store approval is a step that is hard to predict on its own.
Maintenance: New OS versions and user feedback shape the next cycle.
If you want to see what this looks like from an agency point of view, read what a mobile app development company actually does.
SDLC Best Practices
Write measurable requirements. Vague goals create rework later.
Test continuously. Automate tests so every change is checked.
Keep scope visible. Track change requests and decide on them openly.
Document key decisions. When team members change, knowledge should stay.
Review code. A second pair of eyes catches defects and spreads knowledge.
Plan maintenance from day one. Budget for updates, hosting and support.
Measure after release. Use analytics and feedback to decide what to build next.
Common SDLC Mistakes
Skipping requirements: The wish to start fast leads to the most expensive fixes later.
Leaving testing to the end: Defects pile up and the delivery date slips.
Not documenting anything: Knowledge leaves with the team.
Forgetting maintenance costs: Post-launch updates are rarely budgeted.
Forcing the wrong model: Pushing a changing product into a rigid Waterfall plan creates delays.
If you want to assess where your current software stands, our article on what a software audit should reveal lists the issues a good review should surface.